Lightspeed Cloud gives you three kinds of storage: block storage volumes attached to VMs, network-mounted shared filesystems for sharing data across multiple VMs, and S3-compatible object storage buckets for application data, backups and static assets.
Volumes
Every VM has a root volume created automatically at deploy time. You can also create additional data volumes and attach them to a VM - useful for separating application data from the OS disk, or attaching extra capacity later without rebuilding the VM.
Creating and attaching a volume#
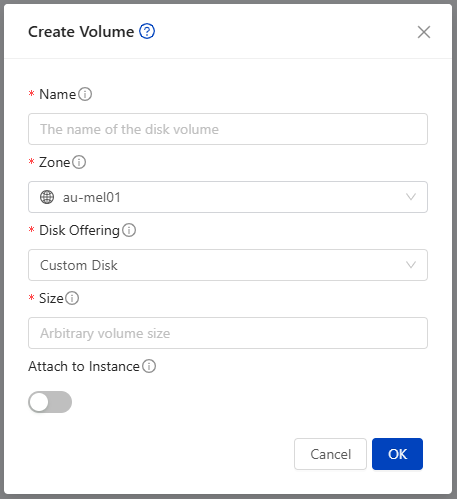
From Storage → Volumes → Create Volume, choose a disk offering (size and performance tier) and the zone it should live in. Once created, attach it to a running or stopped VM; on Linux, you'll typically need to partition, format and mount the new disk from within the guest OS before it's usable.
The number of data volumes you can attach to a single VM is typically 6. If you need more independent disks than that, consider a shared filesystem instead.
Resizing a volume#
Data volumes can be resized upward from the portal without recreating them. After resizing, you'll usually still need to grow the filesystem inside the guest OS to make the additional space usable (e.g. with growpart and a filesystem-specific resize command on Linux).
Resize targets are constrained to the sizes defined by the disk offering you're on, unless it's a custom-sized offering. If you need a size outside what your current offering allows, moving the volume to a different disk offering may be required.
Volume snapshots#
Volume snapshots capture a point-in-time copy of a single disk, backed up to secondary storage. They're useful for protecting data volumes independently of the VM they're attached to, and can be used to create a new volume elsewhere. This is different from an instance snapshot, which captures an entire VM - see Instance and volume snapshots for a full comparison of the two.
Volume snapshots are managed under the Storage menu against the volume itself, not on the instance - this is different from instance snapshots, which are listed on the instance. You can take one on demand from the volume's detail page, or rather than taking snapshots manually, set a recurring snapshot policy on a volume - hourly, daily, weekly or monthly - along with how many snapshots to retain. Once the retention count is reached, the oldest snapshot is dropped as a new one is taken. A scheduled snapshot is skipped if the volume hasn't changed since the last one, so you won't accumulate identical copies of an idle disk.
Uploading an existing volume#
If you have a disk image from outside Lightspeed Cloud, you can upload it directly as a volume and attach it to a VM, rather than starting from a blank disk.
Shared filesystems
Shared filesystems provide a network-mounted filesystem that multiple VMs can mount and access at the same time - useful for shared application state, a common data directory across a cluster of instances, or any workload that needs concurrent access to the same files rather than a volume attached to a single VM.
Creating a shared filesystem#
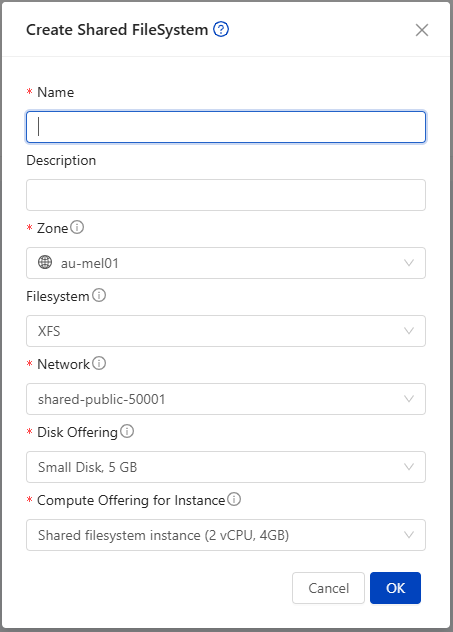
From Storage → Shared Filesystems → Create Filesystem, you'll need to choose:
- A filesystem type - either XFS or EXT4.
- A disk offering - determines the size and performance tier of the underlying storage.
- A compute offering - shared filesystems are served by a small dedicated compute instance that runs in the background, so a compute offering must be selected for it to run on.
Once created, the filesystem can be mounted from any VM with network access to it, using the standard NFS mount options for your guest OS.
Object storage
Object storage buckets provide S3-compatible storage for things like backups, media files, or static website assets, accessible via the standard S3 API alongside the portal UI.
Creating a bucket#
From Storage → Object Storage, create a new bucket and choose a name and quota. You'll be given access keys to use with any S3-compatible client or SDK.
With CloudMonkey, list the available object storage pools and create the bucket in one of them. The quota is in GiB:
cmk list objectstoragepools filter=id,name
cmk create bucket name=my-backups objectstorageid=<pool id> quota=500 versioning=true
The bucket's URL and access keys are shown on its detail page in the portal. Use the URL as the endpoint in your S3 client. The access keys grant full control of the bucket, including its policy, lifecycle rules and retention settings, so store them as you would a password.
Versioning#
With versioning enabled, overwriting or deleting an object keeps the earlier copy as a previous version. A deleted object can be restored by removing its delete marker or by copying back a previous version.
Turn versioning on when creating the bucket, or later from the bucket's Update Bucket action in the portal (cmk update bucket id=<bucket id> versioning=true). Turning versioning off suspends it: versions that already exist are kept, and new writes stop creating versions.
Object lock and retention#
Object lock prevents objects from being deleted or overwritten until a retention period has passed. It protects backups against accidental deletion, and in compliance mode against deletion by anyone holding the bucket's access keys.
Object lock requires versioning. Turn versioning on first, either when creating the bucket or later from the bucket's Update Bucket action (cmk update bucket id=<bucket id> versioning=true). This applies to new and existing buckets.
Object lock is then enabled by applying a retention rule through the S3 API with any S3-compatible client. Once a retention rule is configured, versioning stays on permanently and cannot be turned off. The settings are:
- Retention period - how long each object stays locked, counted from the time that object was uploaded.
- Governance mode - locked objects cannot be deleted by ordinary requests, but a request that explicitly bypasses governance retention can delete them. Suited to guarding against mistakes.
- Compliance mode - nobody can delete a locked object or shorten its retention until the period ends, including the bucket owner and Lightspeed support. Suited to backups that must survive a compromised key.
- Legal hold - an optional per-object lock with no expiry date, which stays in place until it is removed.
The following example uses the AWS CLI to apply a default rule, so every new object in the bucket is locked in compliance mode for 30 days:
aws s3api put-object-lock-configuration \
  --endpoint-url https://<bucket endpoint> \
  --bucket my-backups \
  --object-lock-configuration '{"ObjectLockEnabled":"Enabled","Rule":{"DefaultRetention":{"Mode":"COMPLIANCE","Days":30}}}'
Backup tools that support object lock can also set retention on each object as they upload it. Check the current configuration with aws s3api get-object-lock-configuration.
Deleting a locked object without naming a version adds a delete marker that hides it. The locked version remains stored and billed until its retention expires.
Granting another account access to a bucket#
Each account has one set of access keys. These keys have full control of every bucket in the account. To give a person or system limited access to a bucket, use a second account, referred to here as the grantee account. A bucket policy on your bucket sets what the grantee account may do.
The steps are:
- Create a second account in your domain from Accounts → Add Account in the portal. This is the grantee account. See Domains, Accounts, Users and Projects for how accounts sit within your domain.
- Sign in to the grantee account and create a small bucket. The grantee account's access keys are issued when it creates its first bucket. They are shown on that bucket's detail page.
- Note the grantee account's ID. This is the account's UUID, shown on the account's details in the portal.
- Using your own account's access keys, apply one of the bucket policies below to your bucket.
- Configure the person or system with the grantee account's access keys and your bucket's endpoint and name.
Three permission levels are described below:
- Read-only - the grantee account can list and download objects. It cannot upload, overwrite or delete them.
- Read and write - the grantee account can list, download, upload and delete objects.
- Write-only - the grantee account can upload objects. It cannot list, download or delete them. Suited to backup systems.
In each example, replace my-backups with your bucket name and <grantee account ID> with the grantee account's UUID.
Read-only. Save the following policy as read-only-policy.json:
{
  "Version": "2012-10-17",
  "Statement": [
    {
      "Sid": "ReaderList",
      "Effect": "Allow",
      "Principal": {"AWS": ["arn:aws:iam:::user/<grantee account ID>"]},
      "Action": ["s3:ListBucket"],
      "Resource": ["arn:aws:s3:::my-backups"]
    },
    {
      "Sid": "ReaderGet",
      "Effect": "Allow",
      "Principal": {"AWS": ["arn:aws:iam:::user/<grantee account ID>"]},
      "Action": ["s3:GetObject", "s3:GetObjectVersion"],
      "Resource": ["arn:aws:s3:::my-backups/*"]
    }
  ]
}
Read and write. Save the following policy as read-write-policy.json. The two Deny statements require each upload to give your account full control of the new object. They also prevent the grantee account from changing object permissions:
{
  "Version": "2012-10-17",
  "Statement": [
    {
      "Sid": "EditorList",
      "Effect": "Allow",
      "Principal": {"AWS": ["arn:aws:iam:::user/<grantee account ID>"]},
      "Action": ["s3:ListBucket"],
      "Resource": ["arn:aws:s3:::my-backups"]
    },
    {
      "Sid": "EditorObjects",
      "Effect": "Allow",
      "Principal": {"AWS": ["arn:aws:iam:::user/<grantee account ID>"]},
      "Action": ["s3:GetObject", "s3:GetObjectVersion", "s3:PutObject", "s3:DeleteObject"],
      "Resource": ["arn:aws:s3:::my-backups/*"]
    },
    {
      "Sid": "RequireOwnerAcl",
      "Effect": "Deny",
      "Principal": {"AWS": ["arn:aws:iam:::user/<grantee account ID>"]},
      "Action": ["s3:PutObject"],
      "Resource": ["arn:aws:s3:::my-backups/*"],
      "Condition": {"StringNotEquals": {"s3:x-amz-acl": "bucket-owner-full-control"}}
    },
    {
      "Sid": "EditorNoAcl",
      "Effect": "Deny",
      "Principal": {"AWS": ["arn:aws:iam:::user/<grantee account ID>"]},
      "Action": ["s3:PutObjectAcl", "s3:PutObjectVersionAcl"],
      "Resource": ["arn:aws:s3:::my-backups/*"]
    }
  ]
}
Write-only. Save the following policy as write-only-policy.json:
{
  "Version": "2012-10-17",
  "Statement": [
    {
      "Sid": "WriterPut",
      "Effect": "Allow",
      "Principal": {"AWS": ["arn:aws:iam:::user/<grantee account ID>"]},
      "Action": ["s3:PutObject"],
      "Resource": ["arn:aws:s3:::my-backups/*"]
    },
    {
      "Sid": "RequireOwnerAcl",
      "Effect": "Deny",
      "Principal": {"AWS": ["arn:aws:iam:::user/<grantee account ID>"]},
      "Action": ["s3:PutObject"],
      "Resource": ["arn:aws:s3:::my-backups/*"],
      "Condition": {"StringNotEquals": {"s3:x-amz-acl": "bucket-owner-full-control"}}
    },
    {
      "Sid": "WriterNoReadNoAcl",
      "Effect": "Deny",
      "Principal": {"AWS": ["arn:aws:iam:::user/<grantee account ID>"]},
      "Action": [
        "s3:GetObject", "s3:GetObjectVersion", "s3:GetObjectAcl",
        "s3:PutObjectAcl", "s3:PutObjectVersionAcl",
        "s3:DeleteObject", "s3:DeleteObjectVersion"
      ],
      "Resource": ["arn:aws:s3:::my-backups/*"]
    }
  ]
}
With this policy the grantee account cannot change object permissions or upload objects as public. Your own account keeps full access to every object the grantee account writes.
Apply the chosen policy with your own account's access keys. For example, for the write-only policy:
aws s3api put-bucket-policy \
  --endpoint-url https://<bucket endpoint> \
  --bucket my-backups \
  --policy file://write-only-policy.json
An object uploaded by the grantee account belongs to the grantee account. Your account can read it only if the upload set the bucket-owner-full-control ACL. The read and write and write-only policies therefore refuse uploads without this ACL. Configure the client to send it with each upload. With the AWS CLI and the grantee account's access keys:
aws s3api put-object \
  --endpoint-url https://<bucket endpoint> \
  --bucket my-backups \
  --key <object name> \
  --body <file> \
  --acl bucket-owner-full-control
aws s3 cp accepts the same --acl bucket-owner-full-control option.
Take the following into account:
- Changing the bucket's public or private access setting in the portal replaces the bucket policy. This removes all access granted to other accounts. Apply the policy again after any such change.
- Store your own account's access keys separately from the systems that hold the grantee account's keys.
- For backups, combine the write-only policy with versioning and object lock (see Versioning and Object lock and retention above). A write-only grantee can still overwrite an existing object by uploading another with the same name. With versioning and object lock, overwritten and deleted backups remain recoverable.
Expiring old objects#
Lifecycle rules delete objects automatically once they reach a given age. They are configured through the S3 API. The following example expires objects 30 days after upload and permanently removes previous versions one day after they are replaced:
aws s3api put-bucket-lifecycle-configuration \
  --endpoint-url https://<bucket endpoint> \
  --bucket my-backups \
  --lifecycle-configuration '{"Rules":[{"ID":"expire-backups","Status":"Enabled","Filter":{"Prefix":""},"Expiration":{"Days":30},"NoncurrentVersionExpiration":{"NoncurrentDays":1}}]}'
On a bucket with object lock, a lifecycle rule cannot remove a version that is still within its retention period. Set the expiry to match or exceed the retention period so that versions are removed once their lock ends.
Managing bucket lifecycle#
Buckets can be resized, have their access keys rotated, or be deleted once no longer needed. As with volumes, deleting a bucket permanently removes its contents, so make sure anything important is copied elsewhere first.